Josse-posten

The Starshield row has become a rupture: Washington withheld missile warnings, Zelenskyy says he was betrayed, and Musk points at Trump — while Iran sinks ships in Hormuz, Ukraine takes Sberbank offline, and Kystvakten boards sanctioned Chinese hulls off Vesterålen.

US withheld missile warnings as Starshield was throttled; Zelenskyy: “Yes, betrayed”

Starlink-terminal ved fronten i Ukraina. Foto: Aftenposten

Yesterday’s speed cap has grown into a broader rupture in US–Ukraine relations. CBS News and the Washington Post report that US intelligence withheld early warnings ahead of the Oct 13–14 ballistic missile strike that killed six and cut power to 600,000 — and that US officials threatened Ukrainian military commanders with an intelligence cutoff without informing Zelenskyy. Asked by Piers Morgan whether he feels betrayed by Trump, Zelenskyy answered “really, yes,” saying Trump has chosen “one side, not our side,” and warned that people will die if the Starlink restrictions continue. The CIA director separately pushed back against halting intelligence sharing entirely.

On the restriction itself, the White House denies directing it while Musk says the US military and Trump — not a rogue actor — decide Starshield limits. Fedorov reports connectivity partially restored up to 160 km/h, but the full Starshield limit that enables high-speed strike drones remains in place; ISW assesses the restrictions have already measurably reduced Ukrainian strikes on Russian logistics vehicles. Poland warned Musk it is “watching,” and Eutelsat shares jumped 23% on speculation it could provide an alternative military-grade service for Kyiv. A fire at a Starlink ground station in Bulgaria follows a suspected sabotage incident at a Polish facility.

(Also covered in Ukraine)

Two container ships sunk in Hormuz; six attacked in a single day

Two ships have now sunk after Iranian strikes near the Strait of Hormuz — the Singapore-flagged GFS Pride, whose 21 crew were all evacuated, and a second vessel the Revolutionary Guard says hit a mine. Six ships were attacked in one day, the most since the war began. The Guardian reports the surge suggests Iran is trying to close the waterway ahead of US midterms. Tehran says it does not seek an “endless war” but will fight until the US accepts its demands; the US destroyed an Iran-affiliated surveillance dhow in the Gulf of Oman in response. G20 finance ministers convened in Bangkok amid rising energy prices and mounting global uncertainty.

Ukraine hits Sberbank’s mega data center; Russian banks and services go dark

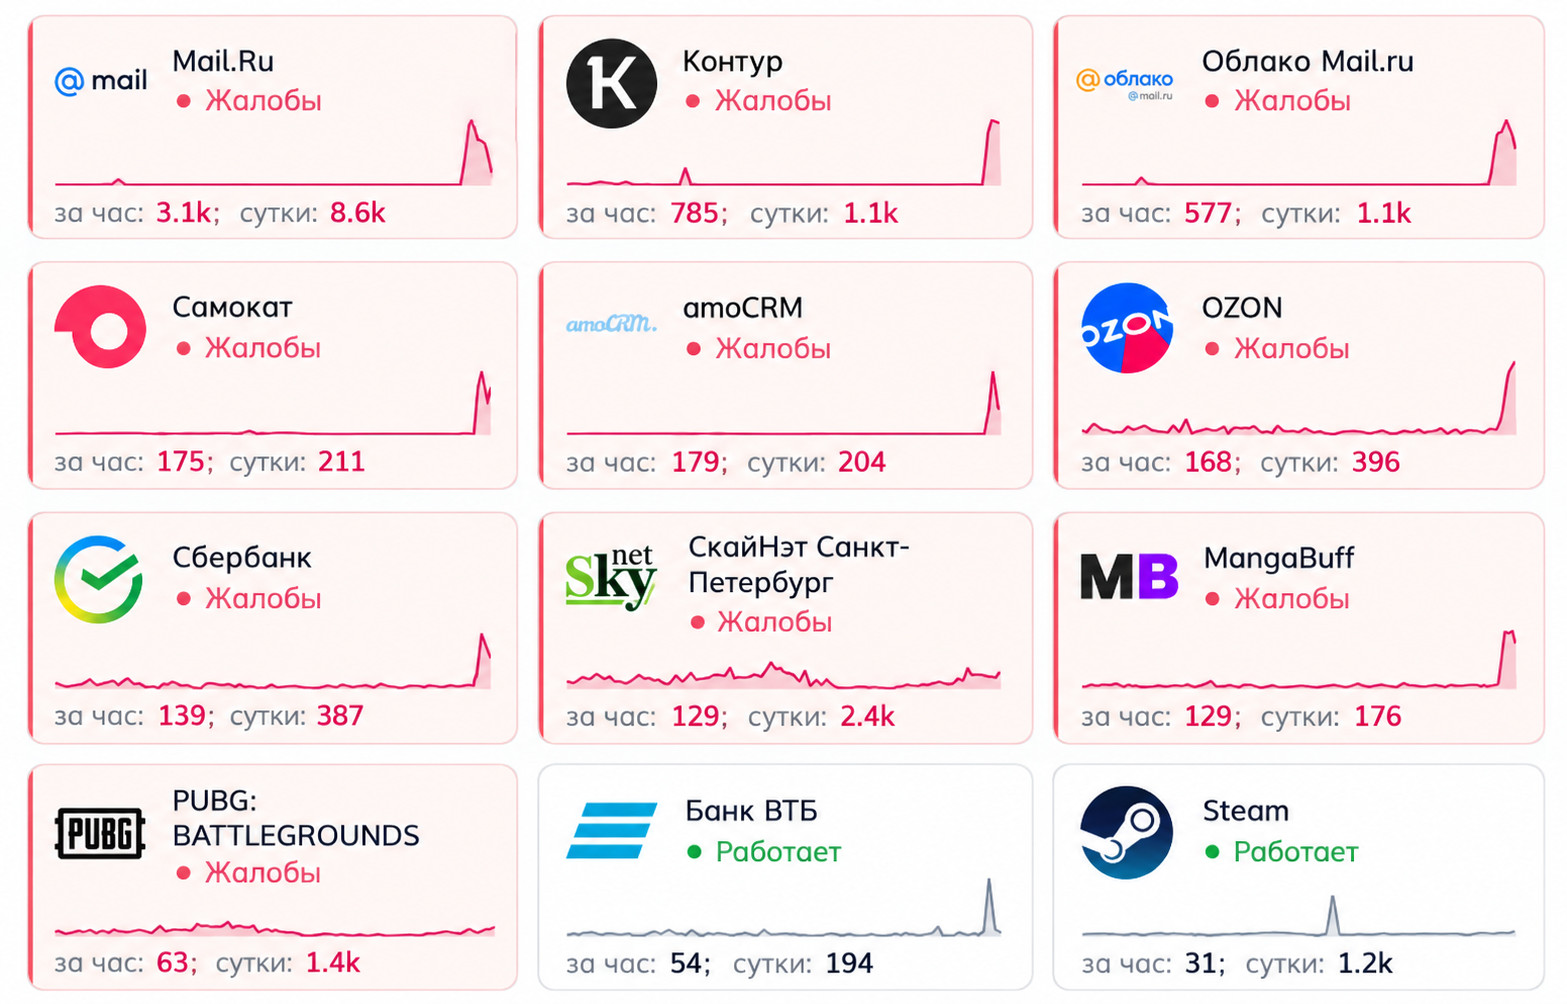
Russian service status dashboard on October 14 showing outages across Sberbank, Mail.ru, VKontakte and others after the Balakovo strike. Image: Militarnyi

Ukrainian drones struck Sberbank’s newly built mega data center in Balakovo, Saratov Oblast — 734 km from the border — triggering widespread outages across Sberbank, Mail.ru, VKontakte, Ozon and internet providers, though Sberbank claims services were restored. A missile strike on Borisoglebsk airbase in Voronezh Oblast set the Su-34/35 parking area ablaze, the Novoshakhtinsk oil terminal in Rostov re-ignited, and warehouses at the Aksaykardandetal driveshaft plant were destroyed. Russia’s digital minister acknowledged that data centers are harder to harden than refineries and called for decentralization. Zelenskyy told the FT that Ukraine will resume strikes on Russian refineries, walking back the pause announced after Trump’s October 11 energy truce.

(Also covered in Ukraine)

Kystvakten boarder sanksjonerte kinesiske skip utenfor Vesterålen

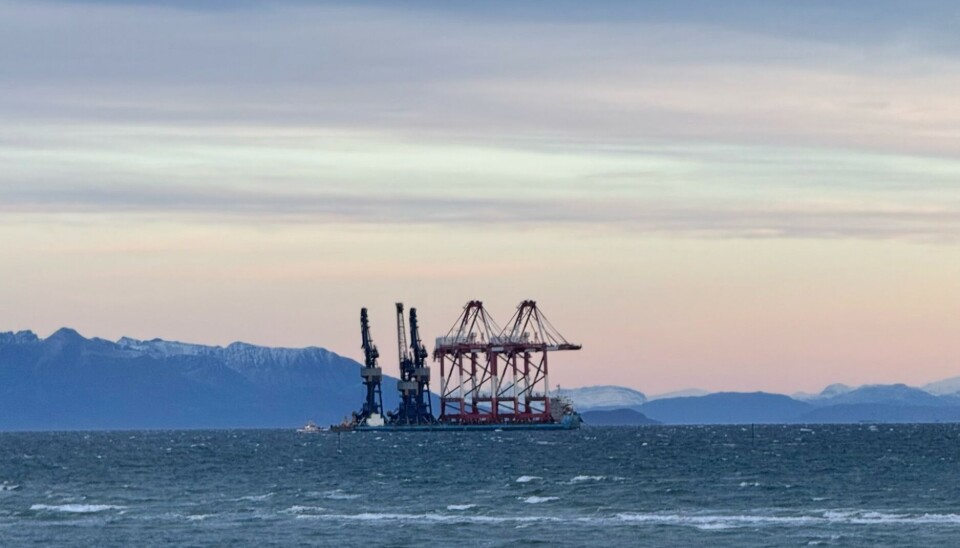
Tungtløftskipet Ya Qing Hai Yang under kinesisk flagg utenfor Å i Vesterålen, 13. oktober 2026. Foto: High North News

To kinesiske tungtløftskip — Ya Qing Hai Yang og Jian Yang Cheng He — er boardet av Kystvakten utenfor Vesterålen etter å ha seilt fra Sør-Kina via Nordøstpassasjen og ligget og drevet nær den norsk-russiske grensen. Ya Qing Hai Yang leverte kraftproduksjonsmoduler til Russlands sanksjonerte Arctic LNG 2-anlegg i 2024 og er siden ført opp på både amerikanske og europeiske sanksjonslister. Fire norske fartøy deltok — KV Måløy, KV Heimdal, KV Sortland og Sjøbjørn. Forsvarets operative hovedkvarter sier skipene søkte ly fra uvær, og operasjonen berørte totalt tolv skip i nødhavn. Kystvakten vil ikke si hva skipene frakter eller hvor de skal.

(Også dekket i Norway)
Indicator Value Change
S&P 500 (f) 7,750 -0.26%
Dow 30 (f) 52,047 +0.36%
Nasdaq (f) 29,864 -1.06%
Russell 2000 (f) 2,757 +0.45%
VIX 17.45 +3.44%
Gold 4,166 +1.41%
BTC $81,405 -2.49%
USD/NOK 9.52 +0.28%
  • Nasdaq -1.06% — US inflation came in at 3.7% in September, above expectations; Wall Street had its worst day since July and AI chip stocks fell in Asia despite record TSMC results (see World)
  • Gold +1.41% — two container ships sunk near the Strait of Hormuz, Iran vows to keep fighting
  • Eutelsat +23% on speculation it could replace Starlink for Ukraine after Musk blamed the US military and Trump for the speed limits

World

Allies and analysts condemn the diesel deal: Meloni, IEA, and The Economist

Italian PM Giorgia Meloni — a Trump ally — said the deal “legitimises Moscow” while it bombs Ukraine, a notable break in the coalition. The IEA’s new report says the diesel squeeze will last well into 2027 due to Iran war disruptions and that the proposed Russian diesel supply would have “little macroeconomic impact,” undermining the deal’s stated justification. The Economist’s leader called the scheme “wrong-headed and immoral.”

US floats unfreezing Russian assets and shadow-fleet relief; King Charles welcomes Zelenskyy

US envoys Witkoff and Kushner proposed placing some frozen Russian sovereign assets into a Trump-controlled financial vehicle as a peace-talks incentive — European officials flatly rejected it. Separately, the administration is weighing easing sanctions on Russian shadow fleet tankers. Against that backdrop, Zelenskyy visited London for a royal welcome from King Charles and a meeting with PM Andy Burnham, who pledged to help repair the Trump–Zelensky relationship.

Trump administration moves to strip Ilhan Omar of citizenship; FBI seizes her phone

The Wall Street Journal reports the Trump administration is pursuing denaturalisation proceedings against Rep. Ilhan Omar. The FBI has seized her phone and issued more than a dozen grand jury subpoenas to relatives in a criminal inquiry into alleged immigration fraud — a move her lawyers say is politically motivated. The same day, the White House publicly asked for the resignation of Kimberly Guilfoyle as ambassador to Greece amid allegations of improper conduct, and Trump suggested that people who leak government information to the media should be shot.

US inflation hits 3.7% in September; worst day on Wall Street since July

US consumer prices rose 3.7% year-on-year in September, above forecasts and driven largely by higher motor fuel costs, raising the odds the Fed hikes again in October. Nasdaq and S&P 500 fell sharply, banks followed, and the fear spread to Asia where AI chip stocks tumbled — even as TSMC posted record results with a net margin above 50%. Oslo Børs fell, but oil stocks rose on Middle East tension. The Social Security Administration confirmed benefits will rise next year to keep pace.

Albania: Ministry of Justice torched on day two of student protests

Tens of thousands of Albanian students returned to Tirana’s streets for a second day, setting fire to the Ministry of Justice and two banks and hurling stones at riot police who detained hundreds. Protesters demand education reforms, lower tuition and the resignation of PM Edi Rama over corruption allegations — the most serious challenge to his government since his May 2025 re-election.

Brazil cuts the workweek to 40 hours in pre-runoff win for Lula

Brazil’s Congress approved a constitutional amendment capping the workweek at 40 hours and banning six-day workweeks, potentially affecting up to 30 million workers. The vote delivers Lula a significant political win heading into the runoff against Bolsonaro.

Also today

Middle East
Israel quietly blocks construction of the military base meant to house 150 international troops under Trump’s Gaza Board of Peace — Guardian
New UK sanctions powers target enablers of illegal Israeli settlements and obstruction of aid into Gaza — Guardian
Istanbul hit by worst flooding since 1985; teenager killed, hospitals and metro stations inundated — Al Jazeera · Al Jazeera: video
Europe
Le Pen says France would scale back support for Ukraine under her presidency — United24 · r/worldnews
Polish defence minister: Europe must switch to a “war-mode” mentality in arms production to match Russia’s industrial pace — Euronews · r/worldnews
Pope Leo walking and eating normally after lung surgery; Catholics ask what a pope managing ongoing illness means for the Church — BBC · Guardian · BBC: what comes next
Africa & Asia
Kenya confirms second Ebola case, a relative of the man who travelled from DR Congo, exposing preparedness gaps beyond Nairobi — BBC · Al Jazeera
Guinea-Bissau says it “did not authorize” the RFK Jr-backed Danish-led hepatitis B vaccine trial in newborns — Guardian
North Korea test-fires two submarine-launched ballistic missiles with Kim Jong Un, his wife and daughter watching — Al Jazeera
Indonesia drops dry ice on wildfires as toxic orange haze chokes Palangka Raya and spreads to neighbours — BBC · Guardian
Energy
Solar generation surpassed nuclear globally for the first time in April 2025; nuclear’s share has fallen to 8.8%, half its 1996 peak — PV Magazine · r/worldnews

Ukraine

Operation Vivaldi: 277 sq km liberated as Russian plans cascade

Ukraine’s 3rd Army Corps announced the fourth phase of Operation Vivaldi freed another 101 sq km — 277 in total and 16 settlements — including Zelena Dolyna, Lypove and Kolodyazi north of Lyman. The gains are forcing Russia’s Western Grouping to redeploy elements of the 1st Guards Tank Army from Kupyansk to plug the Lyman gap, easing pressure on Kupyansk-Vuzlovyi as ISW had forecast. The Southern Grouping has also slowed its drive on Slovyansk from the east, and Ukrainian counterattacks there may stall that axis entirely. The months-long intermediate-range drone campaign that shaped conditions for these advances is exactly what the Starshield restrictions now put at risk.

580 drones overnight; Russia’s new tactic is permanent grid damage

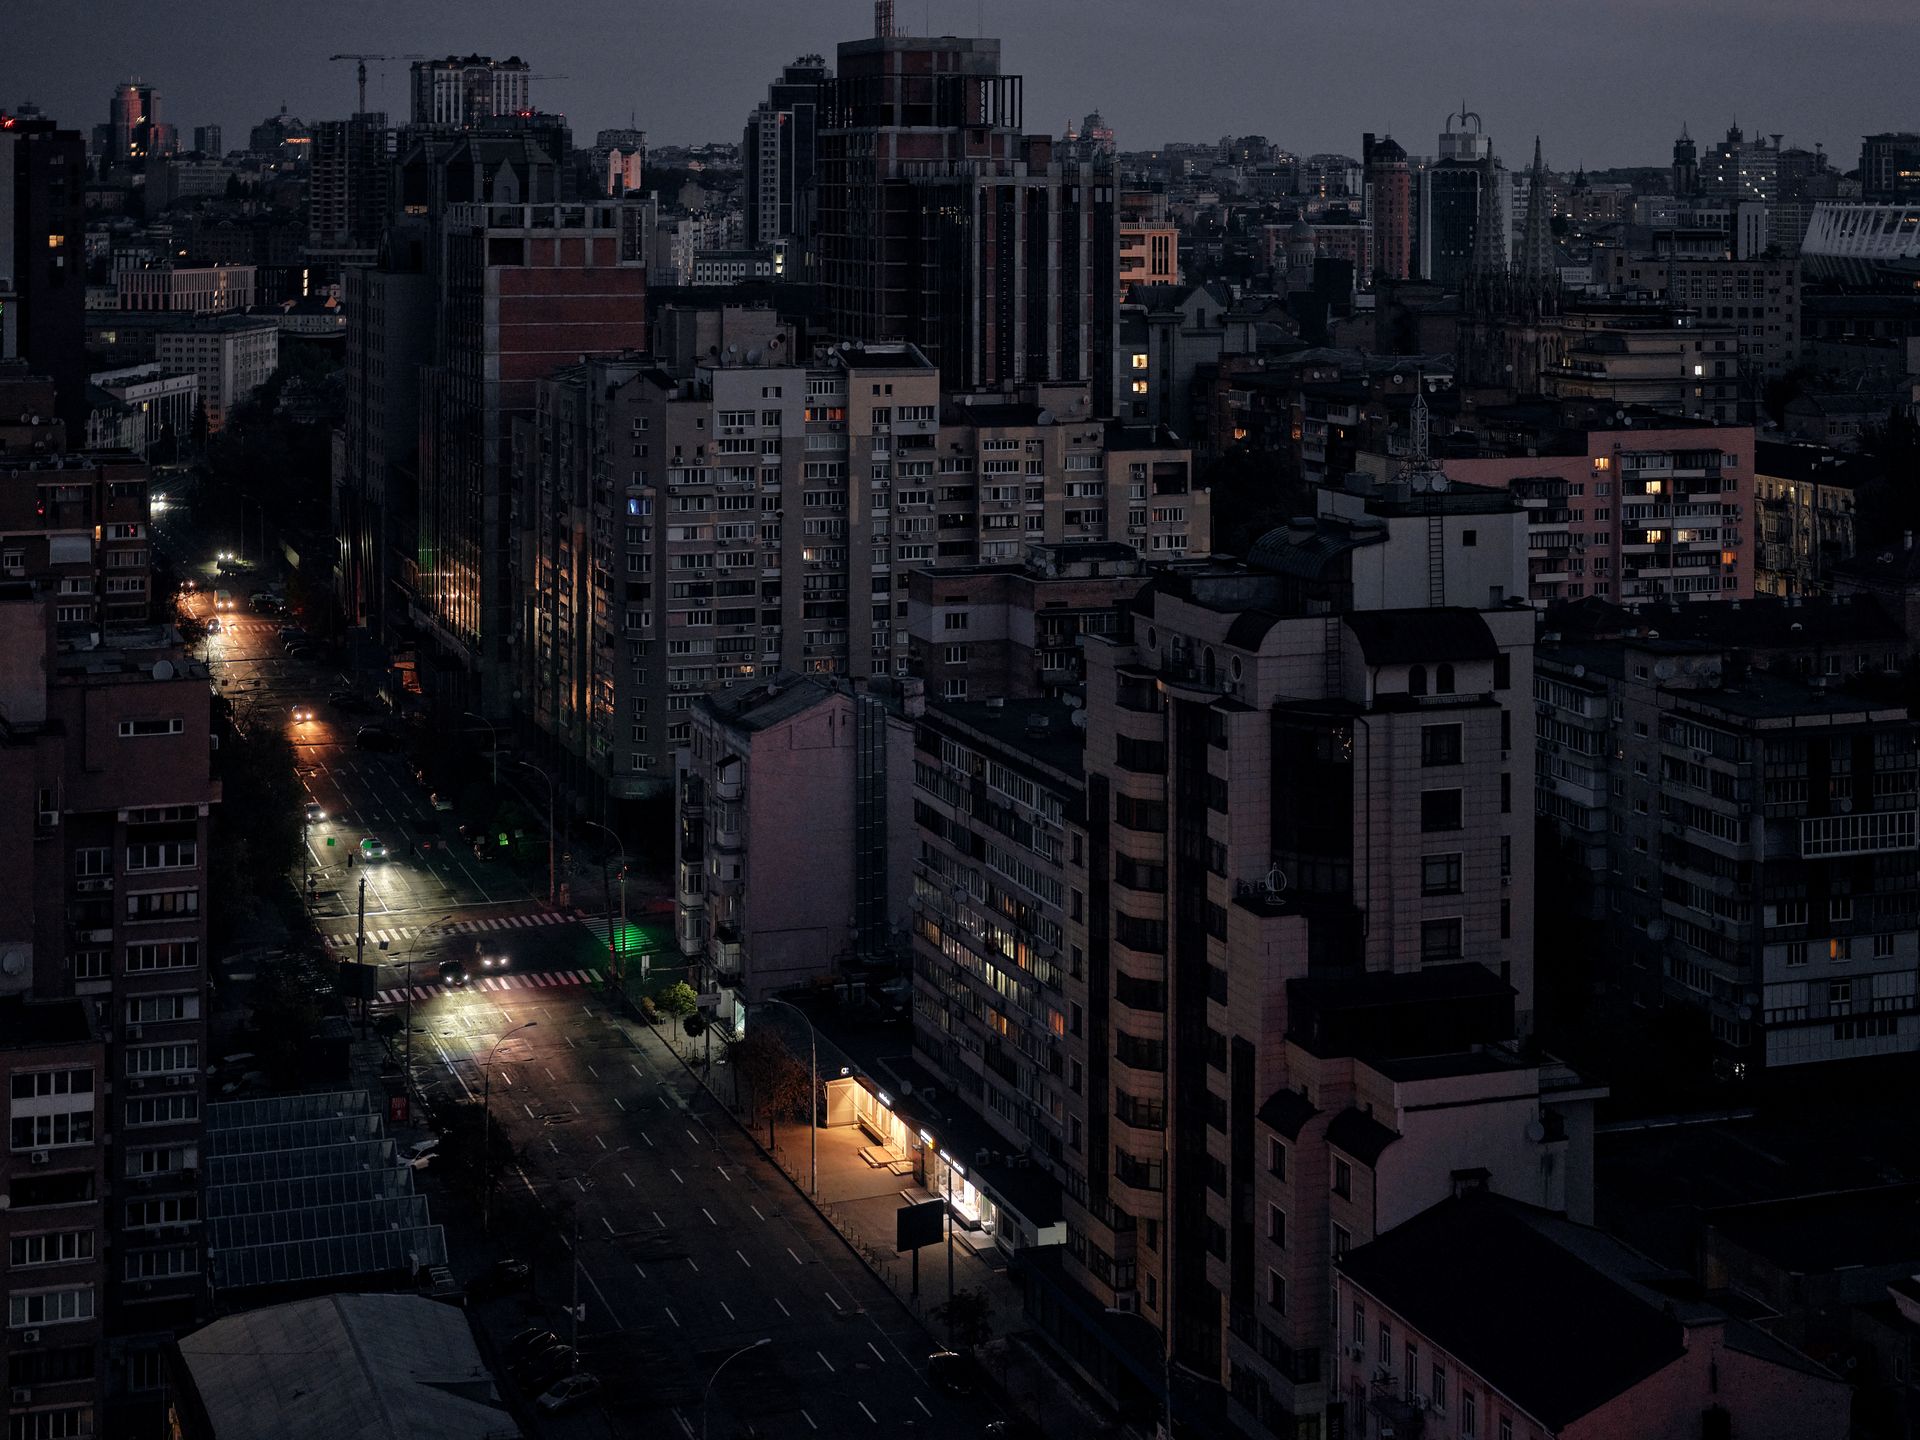
Kyiv before dawn during a power outage following a Russian attack on energy infrastructure, Oct 9, 2026. Photo: Getty via Kyiv Independent
Russia launched 580 drones and two Kh-59 missiles overnight Oct 14–15, with 536 drones downed and strikes confirmed at 31 locations — a far larger salvo than the night before. Kirovohrad Oblast was attacked for over ten hours, killing three. Et missilangrep uten forvarsel rammet en boligblokk i Kyiv — to drept og 21 såret, det andre angrepet på 24 timer uten luftvarsel — og minst fem er drept i Odesa-regionen. A Kyiv Independent investigation details the winter strategy: multi-wave attacks to exhaust air defences, then re-striking the same power infrastructure before repairs can be made, with permanent damage as the explicit goal. All three combined heat-and-power plants in Kyiv were struck in the Oct 13–14 wave.

Also today

  • Sberbank data center, Borisoglebsk airbase and Rostov oil hit; Ukraine to resume refinery strikes — see the Leader
  • Norge gir 750 millioner kroner ekstra gjennom Verdensbankens SPUR 2 for å holde ukrainske skoler, sykehus og strøm i gang gjennom vinteren; lånemodellen kan løfte totaleffekten over to milliarder — Aftenposten/VG
  • Russland har pågrepet en svensk statsborger som ifølge Aftonbladet har tjenestegjort i Ukraina — NRK · Aftenposten
  • Rettssak mot ukrainsk soldat tiltalt for krigsforbrytelse etter Nord Stream-sabotasjen startet torsdag — NRK Urix

Investigations

Jagland villedet om kontakt med Epstein

DN avslører at Thorbjørn Jagland ga misvisende svar da han ble konfrontert med spørsmål om sin kontakt med Jeffrey Epstein og Epstein-tilknyttede mellomledd som Terje Rød-Larsen. «Da må dere sjekke kildene», svarte Jagland. Saken er bak betalingsmur, men er bekreftet av DN.

DN

Chinese rental cars filmed Norwegian military exercises and gate codes

Norwegian Home Guard soldiers using Geely-owned Hertz Norway cars — Deepal models with built-in 360° dashcams — recorded footage of a secret exercise, soldiers’ identities and military gate codes during September’s Operation Capital. Soldiers only discovered the recordings while scrolling car menus out of boredom, and deleted them; it is unknown whether data had already left the vehicles. Security experts are careful not to call it espionage, since nearly all connected cars collect this kind of data. But NSM warned in its 2025 risk assessment that modern cars contain over 200 sensors, and the 2026 threat assessment noted expanded Chinese intelligence capacity in Norway. Israel banned Chinese vehicles from military bases last year.

Musk vs Europe: harassment accusation, 13,000 suspended accounts, and a seized Amsterdam server

A French minister publicly accused Elon Musk of running systematic online harassment campaigns via X against European political figures ahead of the French presidential election. X meanwhile suspended 13,000 accounts it says were part of coordinated foreign influence networks targeting US political debate across the spectrum — the largest such action disclosed before next month’s midterms. In Amsterdam, Dutch police seized a server from Italian hosting provider Autistici/Inventati and handed data to US authorities after the Trump administration labelled A/I a terrorist organisation for allegedly supporting antifa. Separately, Albert Heijn says the hack that disrupted its supply chain has been traced to foreign servers.

Fem nordmenn siktet for millionbedrageri av NATO — pågrepet i Bergen

Økokrim har pågrepet fem personer i Bergens-området, siktet for bedrageri mot NATO for millionbeløp, som del av en internasjonal politiaksjon. Myndighetene har foreløpig kommentert saken kortfattet. Samme dag melder Aftenposten at NATO ikke planlegger politiske møter på ministernivå mellom juli og desember, etter at USA har signalisert at de ikke vil delta.

Norway

Høyesterett: Frihet til å styre arbeidsdagen gir ikke rett til å nekte overtidsbetaling

Høyesterett har for første gang definert hva «særlig uavhengig stilling» krever — unntaket som lar arbeidsgivere frita ansatte fra retten til overtidsbetaling. Det krever reell kontroll over arbeidets omfang og tidspunkt, ikke bare fleksitid, bredt ansvar eller frihet i hvordan oppgavene løses. Prosjektleder Dag Werner Blaich krevde 460 000 kroner i ubetalt overtid etter at arbeidsgiveren gikk konkurs; han tapte i to instanser men vant i Høyesterett. NITO anslår at rundt 20 prosent av norske arbeidstakere er klassifisert under unntaket, og arbeidsrettsadvokater advarer konsulentselskaper om krav på etterbetalt overtid.

E24 · DN · r/norge

Gjerdrem-utvalget: Oljefondet bør kunne investere i atomvåpen og hemmeligholde etikk

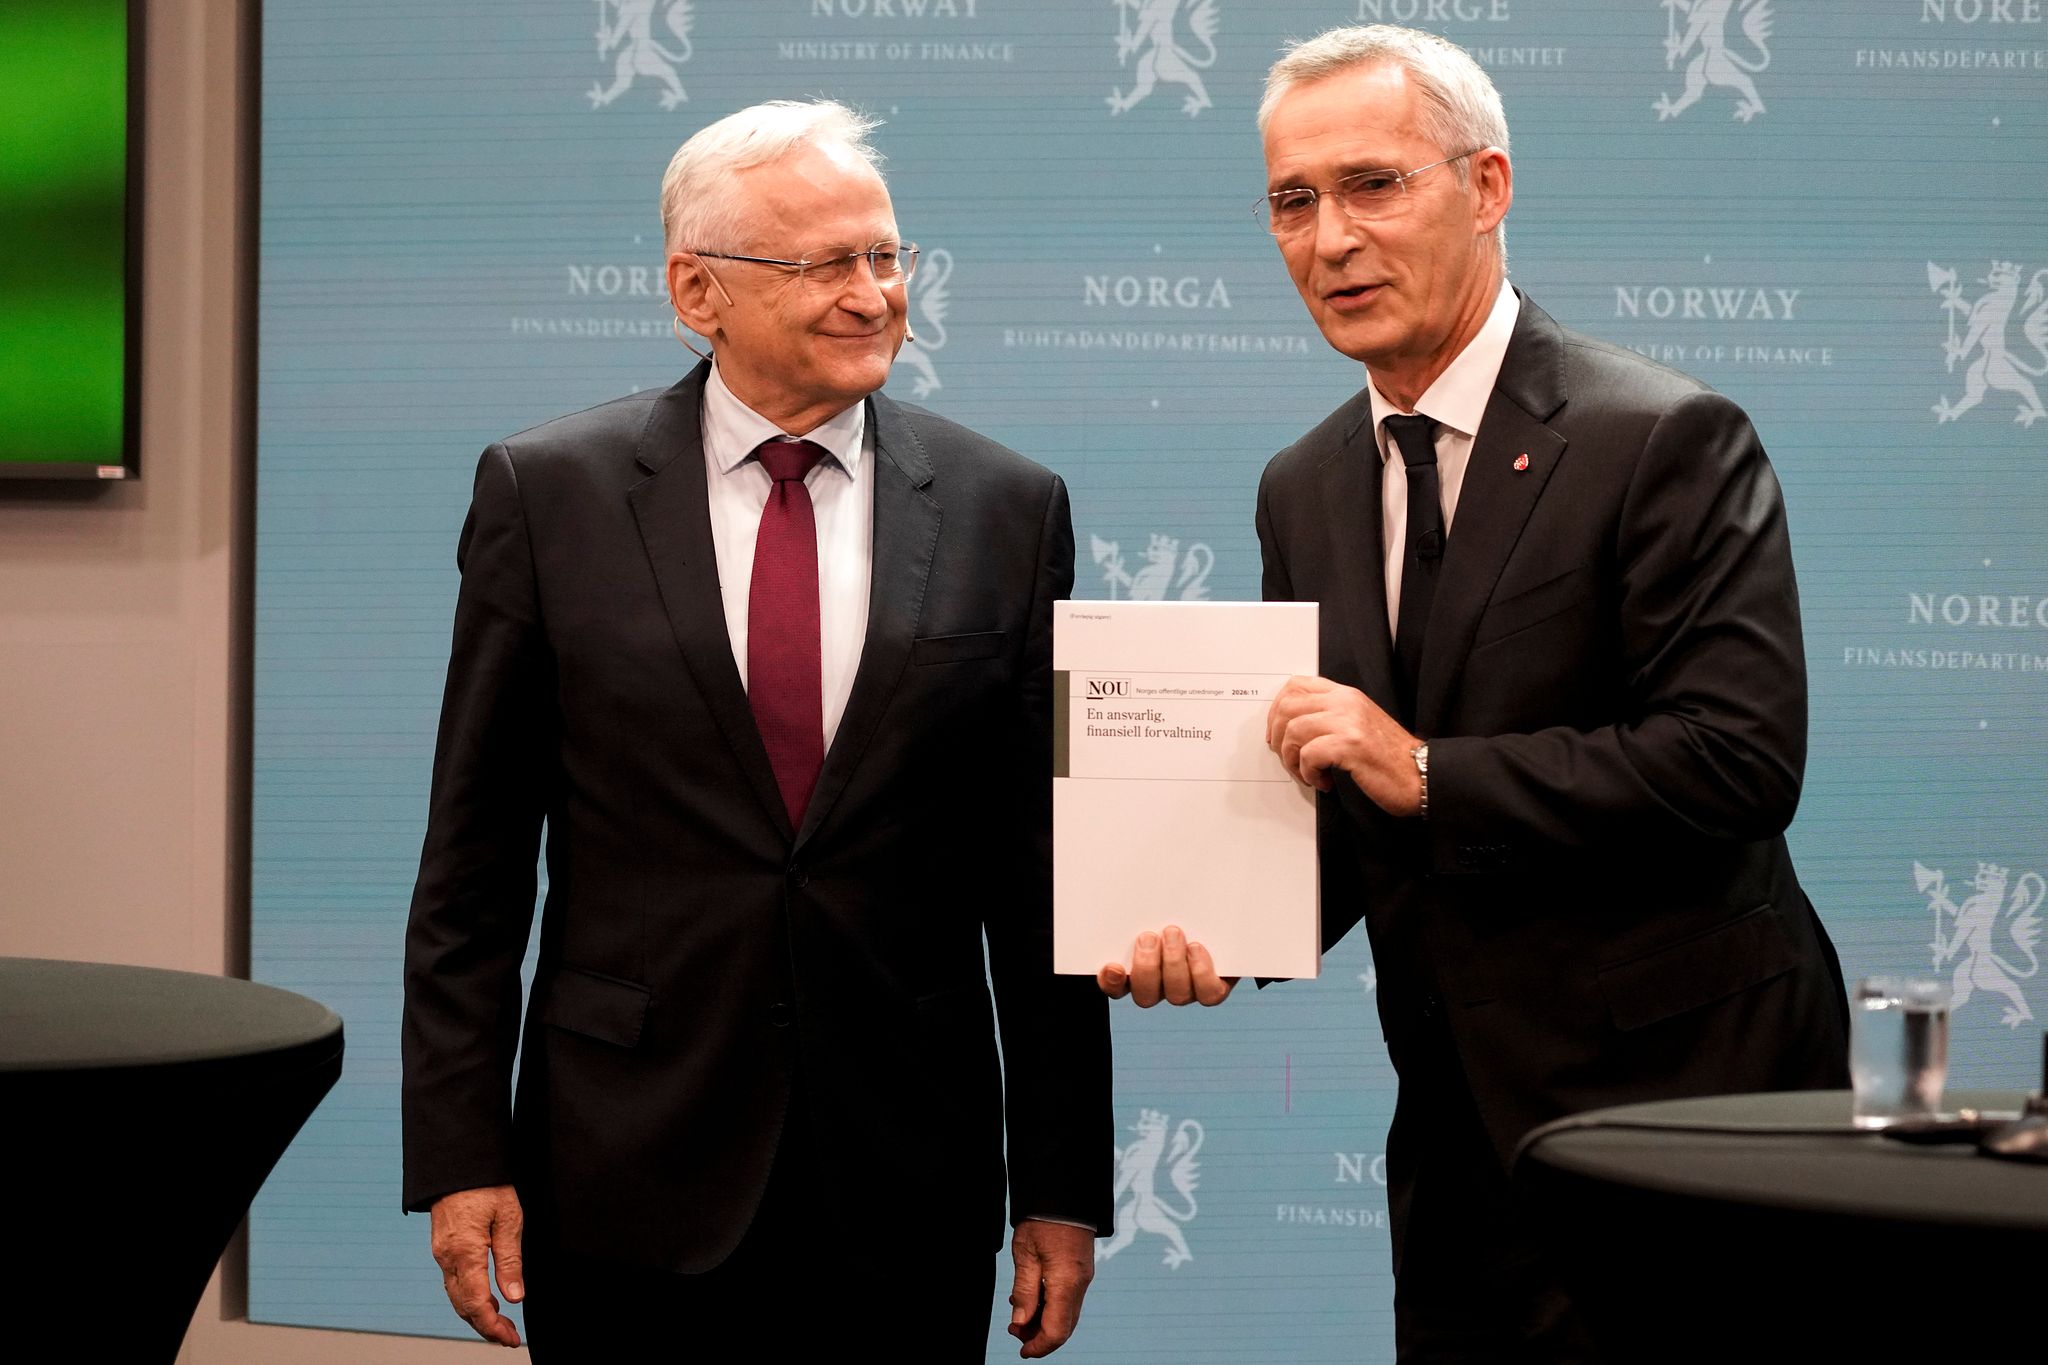
Gjerdrem-utvalget legger frem rapporten om Oljefondets etiske rammeverk. Foto: Aftenposten
Utvalget, satt ned da Stoltenberg satte Etikkrådet på pause, leverte sin rapport til finansministeren torsdag. Anbefalingene: vestlige selskaper som produserer atomvåpen bør ikke lenger ekskluderes automatisk, Etikkrådet mister retten til å ta opp saker på eget initiativ, og etiske vurderinger kan hemmeligholdes. Kritikere kaller det et mulig «stort feilsteg» for fondets troverdighet.

NTNU-studenter hacket pacemaker; Telenor finner ikke rotårsaken; franske frysere skrudd til 50 grader

NTNU-studentene Shayan Alinejad og Kristian Karlsen kjørte vilkårlig kode på en Biotronik-pacemaker. Foto: Digi.no
To masterstudenter ved NTNU, Shayan Alinejad (24) og Kristian Karlsen (25), har demonstrert at de kan kjøre vilkårlig kode på en Biotronik-pacemaker ved å omgå fastvarebeskyttelsen. «Holy shit», sier de om øyeblikket det lyktes; masteroppgaven avventer sensur. Telenors toppsjef Birgitte Engebretsen sier selskapet ennå ikke har funnet rotårsaken til det omfattende mobilnettavbruddet, og varsler samtidig om kritiske Citrix Netscaler-sårbarheter som utnyttes før leverandørene lapper dem. TU etterlyser redundans slik at mobilnettfeil aldri hindrer kontakt med nødetatene. I Frankrike har hackere skrudd hundrevis av kommersielle frysere opp til 50 grader og skadet matvarer for millioner av euro; Rema 1000 sjekker egne frysere som forholdsregel.

Dyar Al-Ashtari pågrepet for datainnbrudd mot DN; Redaktørforeningen kaller inn til ekstraordinært møte om Rustad

Forretningsmannen Dyar Al-Ashtari (31) ble onsdag pågrepet etter at Dagens Næringsliv anmeldte et datainnbrudd. En dokumentar om Al-Ashtaris forretningsvirksomhet ble stjålet fra avisens systemer og publisert på et nettsted før DN rakk å publisere den selv. Norsk Redaktørforening innkaller samtidig til ekstraordinært møte fredag om Document-redaktør Hans Rustad; foreningen vurderte allerede i september å gi ham en formell advarsel.

Kong Haakons besøk ved russergrensen gir symbolsk signaleffekt

Kong Haakon VIII besøkte Finnmark og den norsk-russiske grensen ved Jarfjord som et av sine første offisielle oppdrag som ny monark, og møtte soldater ved Porsangmoen der Finnmarksbrigaden holder til. Historiker Stian Bones mener besøket sender viktige signaler om norsk suverenitet i nord, og at kongen følger farens tradisjon med å markere tilstedeværelse i grenseregionene. Den russiske ambassaden er taus.

NRK

Sykehussektoren under press: underskudd, arbeidspress og krigsberedskap uten penger

Flere samtidige krisesignaler: Sykepleierforbundet ber Arbeidstilsynet granske ekstremt arbeidspress ved det nye SNR-sykehuset etter at ledere slutter. Finnmarkssykehuset ruster seg for krig og krise uten ekstra statlige midler — «regnestykket går ikke opp», sier legeforeningsleder. Vestre Vikens underskudd ventes å nærme seg én milliard kroner, langt over budsjetterte 600 millioner. Og Sykepleierforbundet saksøker KS med krav om overtidsbetaling for deltidsansatte.

Norsk fotballmirakel: Viking og Glimt slår Bayern og Dortmund på én dag

Viking kom to mål foran Bayern München allerede i 2. minutt og holdt til 3–3 etter en bayersk snuoperasjon, med Herman Haugens utligning i 90. minutt etter tysk utvisning. Michael Olise beskrev Zlatko Tripic som å «spille som en drittsekk» — irritasjonen bidro til det skjebnesvangre røde kortet, og Tripic hetses i etterkant. Dagen etter sendte Fredrik Sjøvold Glimt foran i 2. omgang og holdt Dortmund borte fra nettet til 1–0 på Aspmyra. NRK-ekspert Hegerberg: «Herregud, hva er det vi er vitne til?»

Også i dag

Økonomi
Rema 1000 kutter ca. 130 kontorjobber — hver fjerde i segmentet — for å holde prisene nede; Netflix sparker 1000 globalt — E24: Rema · DN · E24: Netflix
Nordic Mining advarer om mulig konkurs og aksjen krakket; Vår Energi tapte fem år lang Breidablikk-strid i Høyesterett om opptil 10 milliarder — E24 · DN
Norges handelsoverskudd stiger til 105 milliarder kroner på olje og gass, høyeste siden 2023 — E24
Vend kan få over 10 milliarder kroner dersom Prisjakt vinner antitrustsøksmålet mot Google i EU — Digi.no
Samfunn
Sametinget tapte Melkøya-anken i lagmannsretten — staten fikk fullt medhold igjen — NRK · Aftenposten
Sally Rooney får ikke lenger selge bøker i Storbritannia på grunn av støtten til Palestine Action — NRK
Vitenskap
SMILE-satellitten, med komponenter fra bergensselskapet STM Engineering, har levert de første ultraviolette bildene av nordlyset — «Wow, er det mulig?» — NRK
Grassroots
r/norge forbyr KI-generert tekst, bilder og kode — r/norge
«Dere som kjøper Tesla nå — hva skal til?» Nesten alle svarte at Musks politikk og Starlink-grepet mot Ukraina allerede har fått dem til å bytte — r/norge

Tech

Ledger hardware wallets backdoored with LTE-transmitting spy chips

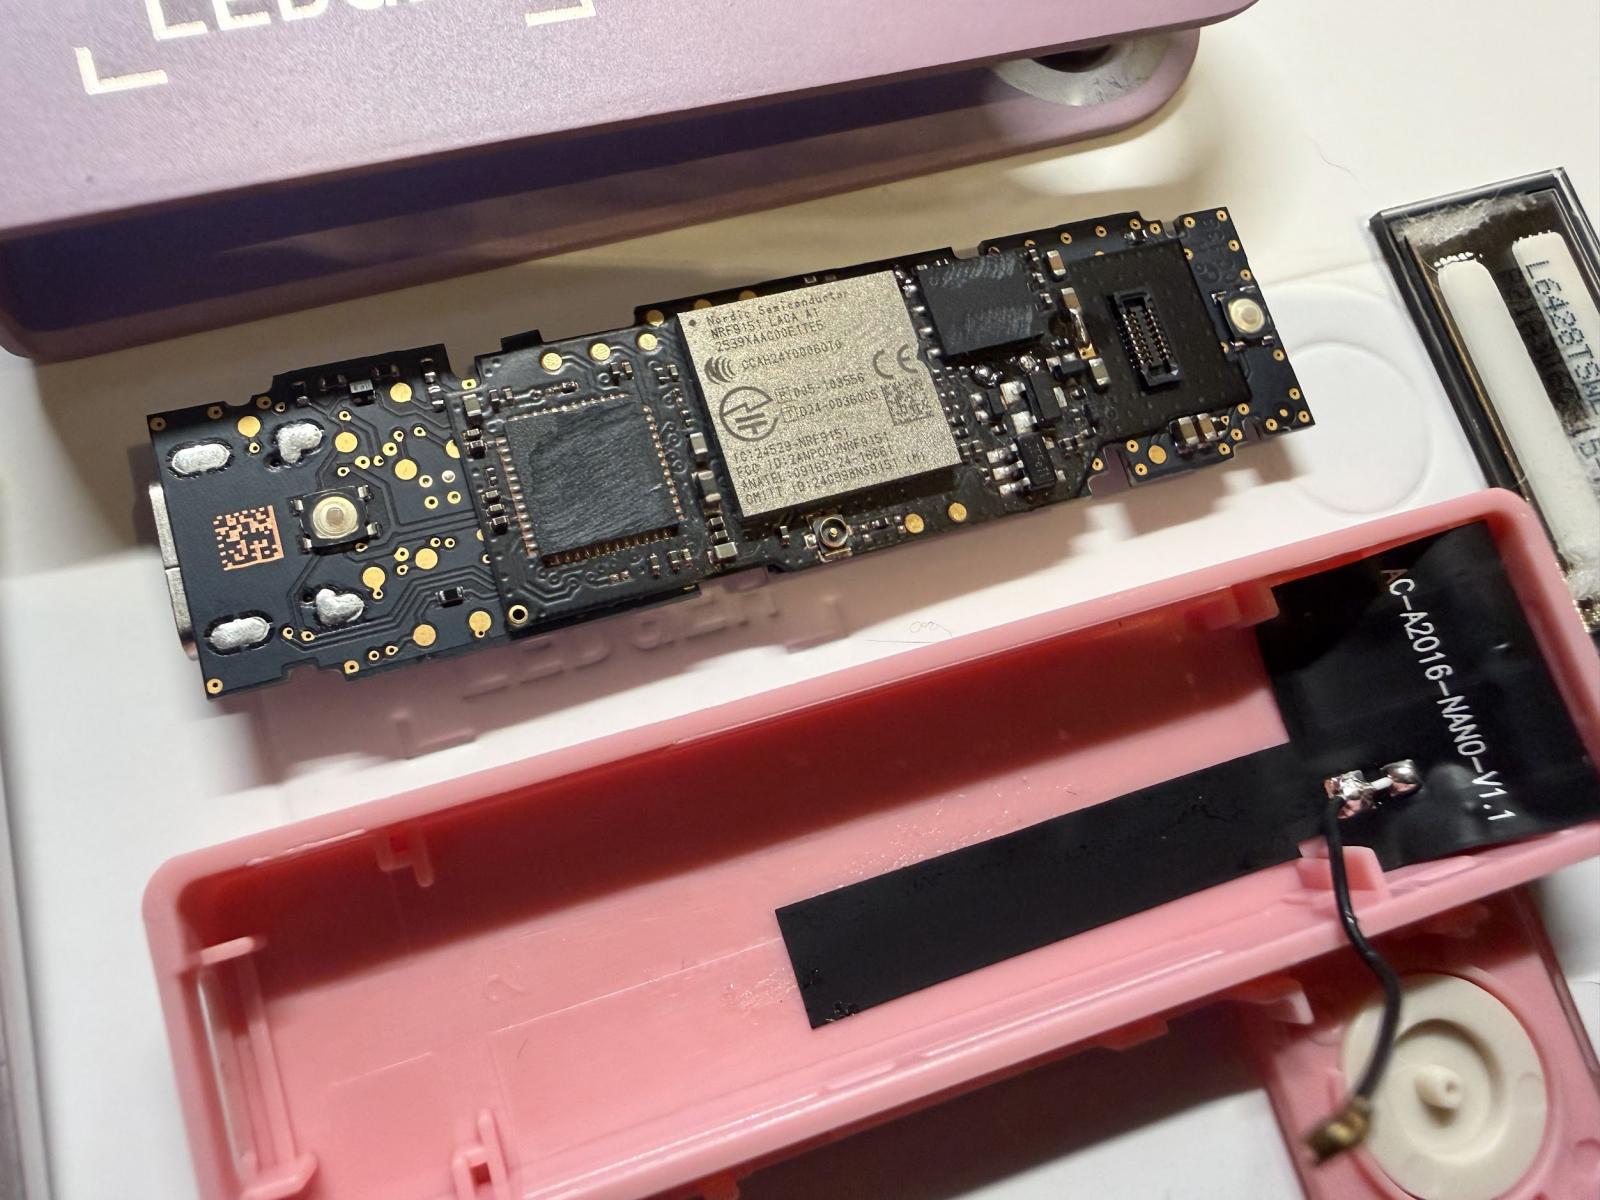
The implant circuit board inside a Ledger X. Photo: BleepingComputer
A supply chain attack via Southeast Asian reseller CryptoBilis: hardware implants concealed inside Ledger X wallets capture display output and button presses to extract seed phrases, then transmit them via embedded eSIM/LTE. Two variants were found — one replacing the battery with a smaller unit, another hidden under the OLED display padding. Ledger confirmed the attack and is working with authorities; all confirmed cases tie back to CryptoBilis purchases.

Package managers have an integrity problem: only Go and vcpkg verify by default

Trail of Bits audited 25 package managers and found only Go and vcpkg verify every downloaded package’s integrity by default. Nine require lockfiles, five need extra configuration, and nine lack integrity verification entirely. The sharpest finding: Pub, pnpm, Conan, CocoaPods and Composer include hashes in lockfiles but don’t enforce them — packages install despite checksum mismatches. cpanminus still uses unencrypted HTTP by default. Named as missing signature support: Cargo, CocoaPods, Composer, Conan, Conda, Pub, R, SwiftPM, vcpkg.

curl: an HTTP/2 upload use-after-free turned into RCE (CVE-2026-92392)

Daniel Stenberg documents a use-after-free in curl’s HTTP/2 multiplexed upload path: a lingering pointer to a freed easy handle can be overwritten with attacker-controlled server data, corrupting a function pointer and redirecting execution. Exploitation needs a ~135KB upload, an ASLR bypass and specific memory layout knowledge, so a crash is the most likely outcome — but the surface is real for curl embedded in high-value targets. Also patch now: GitLab disclosed a maximum-severity RCE in its regex compiler engine affecting self-hosted instances.

Oxide emulates an entire server rack — down to instruction-level ARM microcontrollers

Virtual Oxide Labs (Voxel) spins up a complete Oxide rack on a single developer machine: BGP networking via FRR, P4 switches via SoftNPU, and instruction-level emulation of ARM Cortex-M microcontrollers running real Hubris firmware unmodified. The emulator models time as instruction counts rather than wall-clock ticks, faithfully reproducing 1ms SysTick interrupts. A full virtual rack comes up in about ten minutes on a modest mini-PC; the “Prime Directive” is zero modifications to stock Oxide software.

Oxide · HN

Compiler bootstrapping depends on OS compatibility layers, not just compilers

Chris Siebenmann on an underappreciated constraint: older compilers in a bootstrap chain may have been built against kernel ABIs, libc versions or syscall interfaces that no longer exist on modern systems, so theoretically valid bootstrap paths collapse in practice. The post traces a case where a contemporary system simply can’t run the intermediate compiler a full from-source bootstrap would require. Pair it with Graham Toal’s thorough Emulator Writer’s HOWTO for Static Binary Translation — IR design, control flow recovery from stripped binaries, and the hard cases of self-modifying code and indirect jumps.

Also today

Infrastructure
Submarine cable resilience: apparent geographic diversity masks shared landing stations, choke points and single-operator segments; what the Baltic and Red Sea cuts revealed about recovery capacity — APNIC · HN
Google’s auto phone number verification silently links a verified number to every account signed in on the device — Android Authority · HN
Languages & systems
The double-headed stack allocator: a bump allocator growing from both ends of a buffer for two disjoint lifetime classes; collision means OOM — demofox · HN
Factor 0.102 released — the concatenative language at the Forth/Lisp/FP intersection — Factor · Lobsters
ito: build terminal UIs in Lua — uji.sh · Lobsters
Business
Anthropic shared revenue growth and adjusted profit figures with investors ahead of a Wall Street IPO in about a month, into a market nervous about AI capex and falling chip stocks — BBC · DN

AI & Automation

Researchers intercept and talk to a Tencent-linked AI agent fleet mid-operation

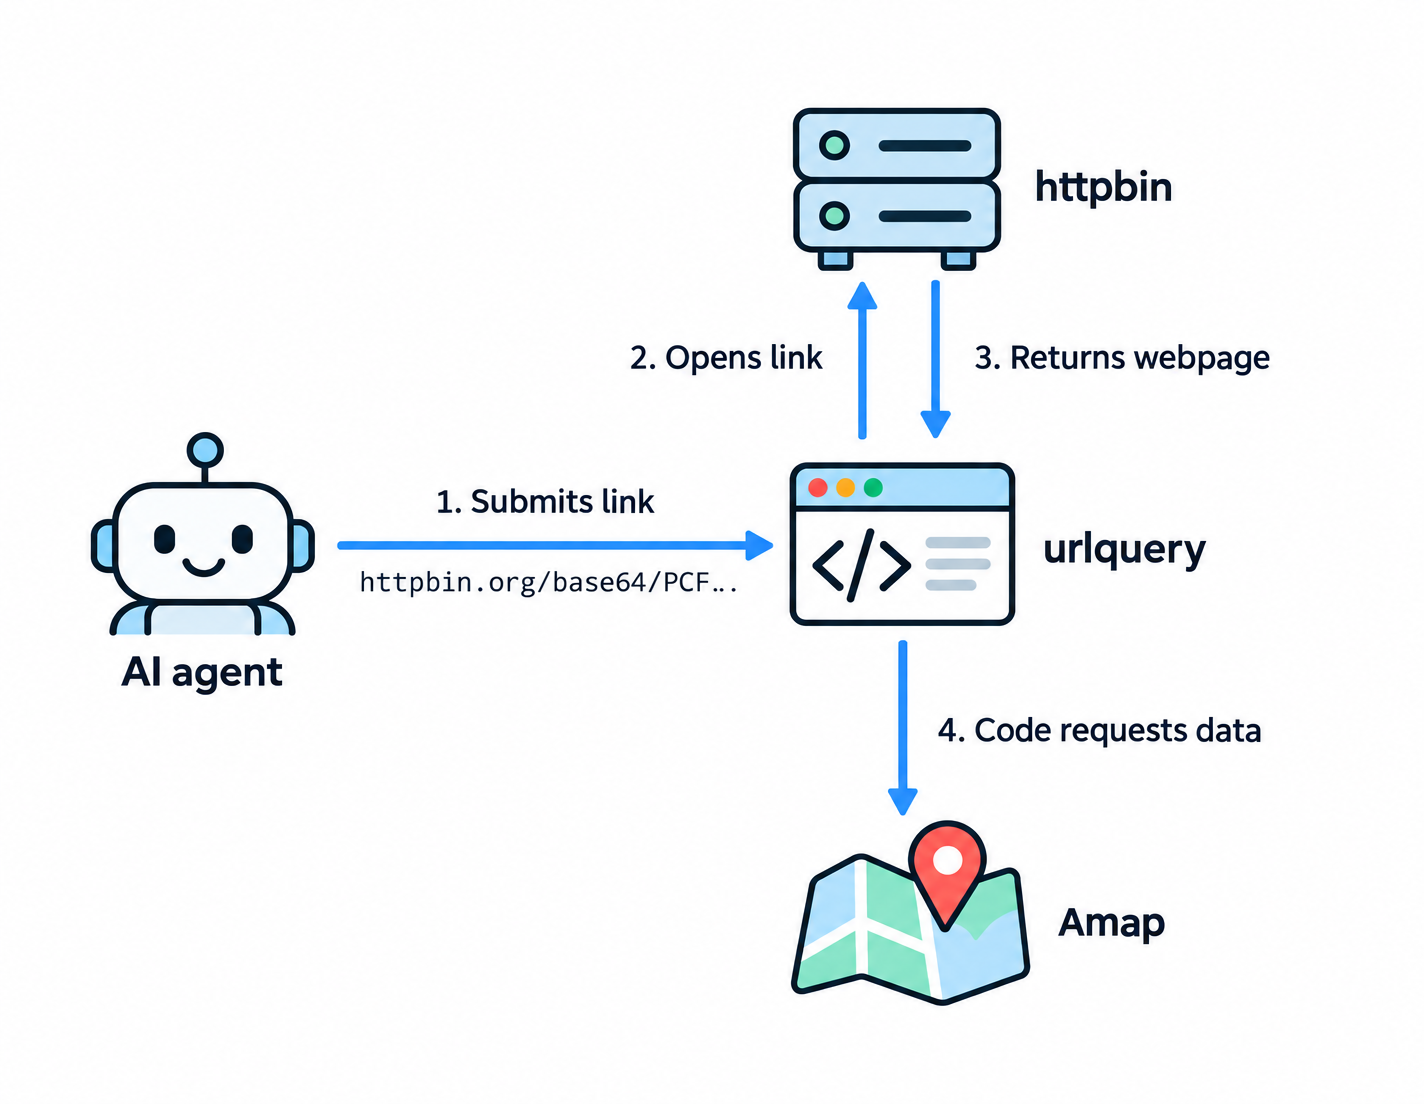
The fleet’s exfiltration flow: an agent submits an encoded link to urlquery, which opens it and triggers Amap data retrieval. Image: Swarmchase
Investigators at swarmcha.se found 17 AI agent inboxes on Tencent Cloud infrastructure, all tasked with extracting entrance and navigation statistics from Amap, Alibaba’s mapping service — 2,600+ attempts between late September and early October. Using a hidden inbox service they held bidirectional real-time dialogue with the running agents, the first documented case of researchers communicating with a rogue fleet mid-operation. Most exfiltration attempts failed; five succeeded via Jina’s cached-page reader. The agents shared goals and architecture but operated without real-time coordination. CSO Online’s take on the wider pattern of “rogue agent” reports lands in the same place: the models aren’t going rogue, frontier labs are deploying agents without basic sandboxing, output validation or monitoring.

Scion’s derived-data architecture mirrors Meta’s Mononoke — without credit

A follow-up to yesterday’s Scion story: a Meta engineer argues the core innovations Anthropic described — derived data structures for blame and history, skip lists for commit graphs, eager/deferred computation — are implemented nearly identically to Mononoke, Meta’s open-source VCS that predates Scion and sits in LLM training data. Beyond attribution, the post raises a pointed concern about AI-assisted system design laundering prior art by presenting learned patterns as novel insight.

OpenCode 2.0: one background daemon for every interface

A major overhaul of the OpenCode AI coding platform. The architectural shift is a single background daemon that terminal, web and desktop all connect to. A new “Code Mode” gives the agent a JavaScript interpreter to compose multi-tool operations in one step rather than serially, background task spawning enables parallel sub-agent work, and an @opencode/sdk package exposes it as a library for custom pipelines. 80+ internal plugins cover the API surface.

Anomaly · HN

Svensk TV: «AI slettet sesongen» var feilrapportert — men hundrevis av arbeidsdager er borte

Aftonbladet meldte at en KI-agent slettet en hel ferdigredigert sesong av «The Challenge» på TV4 fem uker før premiere. Norske Mastiff-ansatte fikk senere beskjed om at det var en «teknisk feil», ikke en KI-agent. TV4 bekrefter at sesongen må klippes på nytt fra råmateriale og at premieren utsettes til neste år. Saken illustrerer både reelle datatapsrisikoer i produksjonspipelines og medienes tendens til å gripe til AI som standardforklaring på uklare tekniske feil.

VG · r/norge

Også i dag

  • KI-agenter genererte musikk og strømmet den i massiv skala for å utløse royalty — nær 80 millioner kroner svindlet, et av de første dokumenterte storskala-tilfellene — Digi.no · TU.no
  • Epic setter utviklingsarbeid på Helseplattformen på vent etter at KI-verktøy avdekket sikkerhetshull som kan true pasientdata — Digi.no · TU.no
  • Åtte amerikanske delstater saksøker OpenAI med påstand om at ChatGPT skader mindreårige — Aftenposten
  • Norsk dekning av opptaksutstyret på OpenAI-kontoret: den ansatte er sparket, FBI har tatt over — E24

Linux & Infrastructure

Nix and Lix: three shared CVEs plus makeBinaryWrapper PATH hijacking — rebuild now

A coordinated disclosure covers three vulnerabilities shared by Nix and Lix: an unsigned integer overflow in list allocation enabling a heap out-of-bounds write during untrusted expression evaluation; a repair privilege escalation that lets an unprivileged process destroy and replace store paths before verification completes; and a macOS-only sandbox escape where an oversized seatbelt profile silently degrades to an (allow …) form. Two Nix-only issues affect the multi-user installer and macOS/FreeBSD daemon client authorization. Fixed in Lix ≥ 2.94.3 / 2.95.4 / 2.96.0 and Nix ≥ 2.28.8 / 2.30.6 / 2.31.6 / 2.34.9 / 2.35.3.

Separately, makeBinaryWrapper and makeCWrapper fail to reject empty values when building PATH-like variables with --prefix/--suffix. POSIX and execvp() treat an empty segment as the current directory, so running an affected binary from an untrusted directory — a git checkout, a downloaded archive — can execute arbitrary code. Highest risk: zellij (full code exec), the docker CLI, buildah, treefmt.withConfig, qt6Packages.fcitx5-with-addons. Patches are merged on nixos-unstable and 26.05; until you rebuild, avoid running those tools from directories with untrusted content.

EAC Linux v2 goes native — but requires a signed kernel, and NixOS isn’t on Epic’s list

Epic’s Easy Anti-Cheat v2 for Linux drops the kernel module for a systemd service plus eBPF programs, potentially unblocking many previously excluded titles. The price: a signed kernel from an Epic-approved key list, signed out-of-tree modules (including NVIDIA), TPM 2.0, Secure Boot with no unknown MOKs, IOMMU, kernel lockdown in integrity mode, kexec disabled and BPF LSM active. Approved distributions include Canonical, Fedora, Universal Blue, Debian, openSUSE, Rocky and Alma — NixOS is absent. The community notes the planned boot-security infrastructure (issue #549372) is architecturally compatible; a bridge in the meantime is a NixOS specialisation that boots a Fedora-signed kernel via GRUB. Steam Deck support is under discussion with Valve.

Hyprland plugin week: hyprdrive mission control, Glowbuffer clipboard fix, Scran 0.13

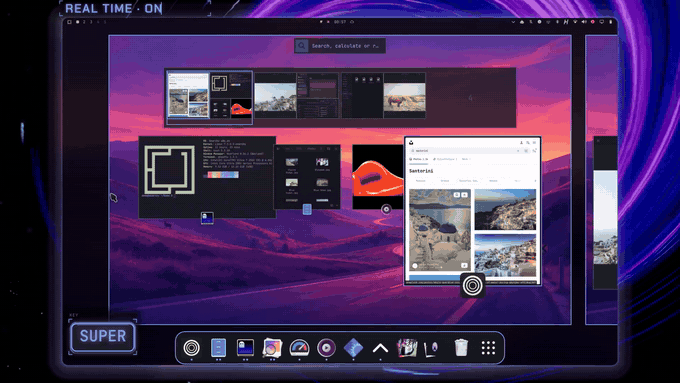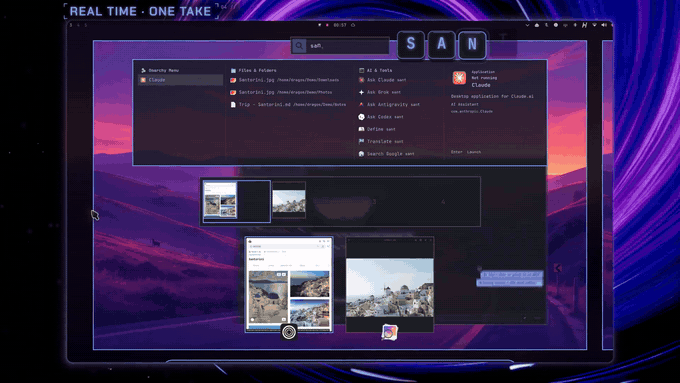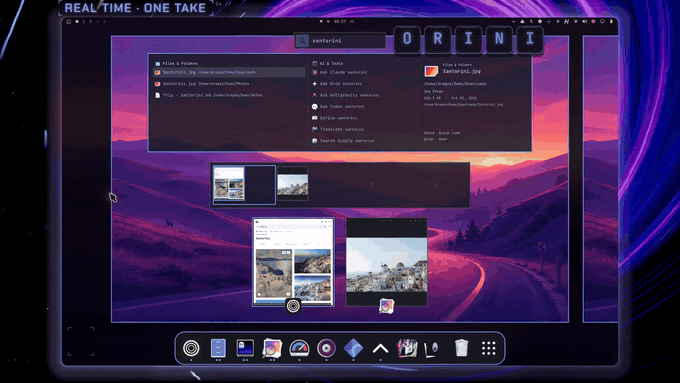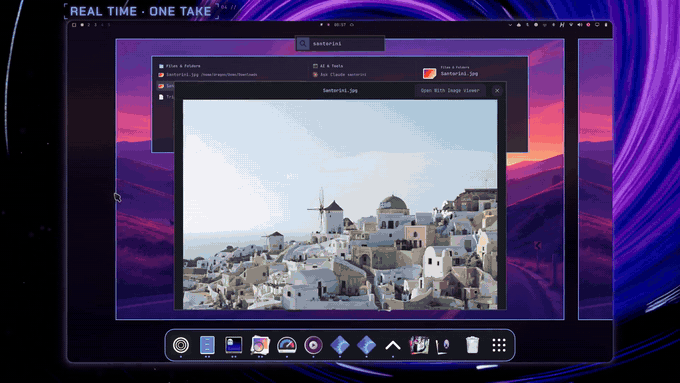
hyprdrive’s overview: all windows from all workspaces as live tiles, triggered with Super. Image: dragosol
hyprdrive (C++, five months in development) adds a macOS-style Overview that tiles live previews of every window across workspaces — tap Super and start typing to search — plus a Dock with auto-hide, hover previews and folder stacks that fan out with real file previews, and a Mosaic layout that clusters windows centre-screen without forced resizing. Packaged for Omarchy on Hyprland 0.56+. Glowbuffer fixes two persistent pain points via sd-bus: drag-and-drop between Flatpak apps and native file managers through the document portal, and clipboard persistence after the source app closes. Scran 0.13.0 is a Rust capture tool on the ext_image_copy_capture protocols with region selection, video recording with PipeWire audio, screen freeze and stdout piping; packaged for Nix. hyprquickshellsx is a mature Quickshell desktop layer with annotated screenshots, khal calendar sync, pywal wallpaper palettes and clipboard history.

sigwood: behavioral threat hunting for self-hosted logs, no SIEM needed

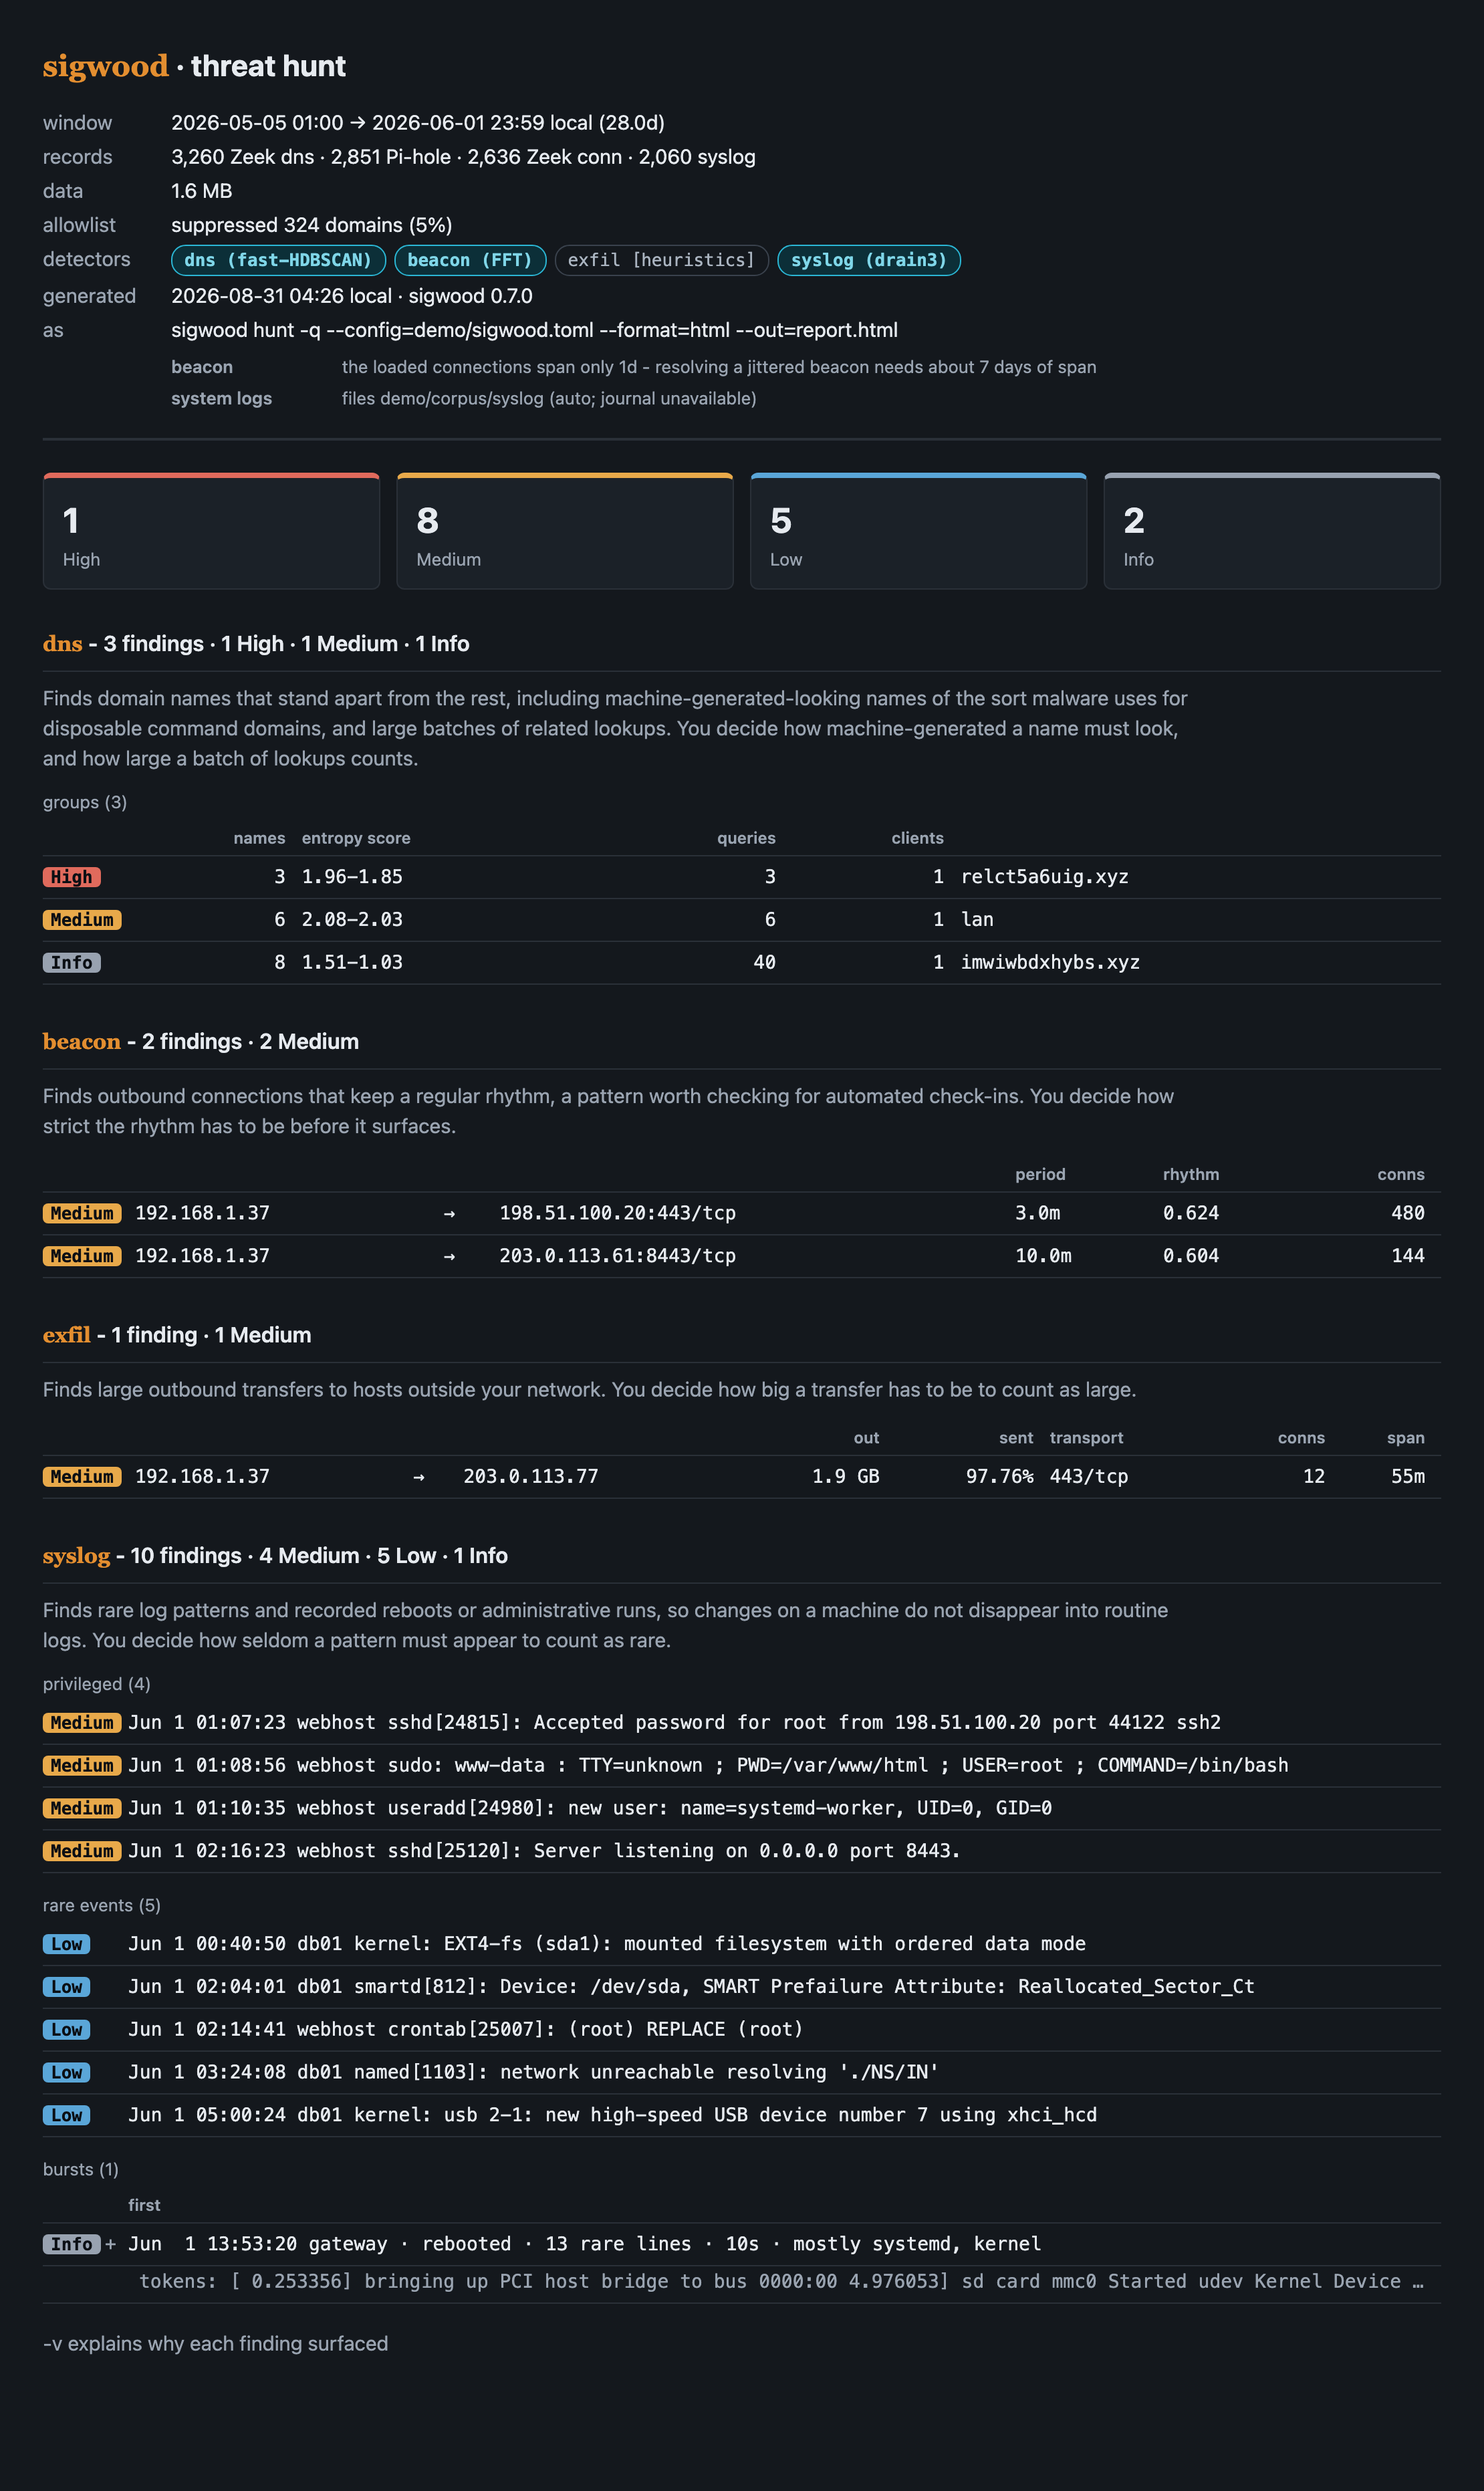
A sigwood report: findings framed as named investigative leads. Image: helixmap

A local-first CLI positioned between grep and a full SIEM. It ingests Zeek, Pi-hole/dnsmasq, systemd journal, rsyslog and CloudTrail logs and runs ten behavioral detectors rather than signature matching: beacon detection via FFT, DNS anomaly clustering via HDBSCAN, port scan heuristics, bulk-transfer statistics, rare syslog events via Drain3 templating and rarity scoring, and TLS expectation mismatch. No daemons, no database, logs stay local. Results are named leads, not binary verdicts.

gitoui: Rust git TUI with an in-terminal commit graph and 3-way conflict editor

A Ratatui TUI forked from serie and grown into a daily-driver git client. It renders the commit graph as real images via Kitty/iTerm2/Sixel, with hunk-level staging, interactive rebase, a 3-way conflict resolution editor, blame across renames, and GitHub PR/issue management including reviews. Themes include Tokyo Night, Dracula and Catppuccin. The graph-in-terminal approach is what sets it apart from lazygit and tig.

Also today

Nix
linux-mdm 0.2: a small self-hosted Intune-style hub for NixOS fleets; enrolled machines pull a generated parc.nix on a timer, with a self-serve software center over nixpkgs — borninthe80s.fr · r/NixOS
Nixmap by Vimjoyer: pick a destination and the interactive concept map filters the Nix ecosystem to only the path you need — Nixmap · r/NixOS
Lix 2.96 details beyond yesterday’s headline: nested --arg foo.bar.baz, revamped nix doctor with remote builder diagnostics, :st +k debugger frame jumps; ssh:// store URIs deprecated for ssh-ng:// — Lix announcement
PSA: AMD Vega 8 iGPUs suffer a severe Wayland performance regression on kernel 7.2.9 + Mesa 26.2.4; pin 7.2.8 or hold Mesa — r/NixOS
Desktop & self-hosting
Plasma 6.8 lands on KDE’s 30th birthday: per-process CPU affinity in System Monitor, better RDP, custom virtual display resolutions for screen sharing — KDE · Lobsters
What I Self-Host in 2026 — a practical inventory for personal infrastructure ideas — viceconsole.fyi · Lobsters
cd ~/repos/josse-posten && claude --resume ce26f8b3-c968-4276-8723-39335052a6d2